How Tokenized Corporate Bond Platforms Should Handle Credit-Rating Changes
A rating downgrade lands on a Friday evening. Your corporate bond tokenization platform holds twelve thousand retail wallets, half a dozen custodian nodes, and an issuer dashboard that nobody updated. Who catches it? How fast? And does the ledger reflect it correctly before Monday’s trading opens? These aren’t hypothetical questions for teams running live bond infrastructure. This article looks at the operational mechanics behind rating-change events, and why getting this workflow wrong creates real data-integrity risk for corporate bond tokenization platforms.
Most discussions about bond tokenization focus on issuance, settlement, or investor onboarding. Rating-change handling gets skipped entirely, treated as “just another data feed.” It isn’t. A credit rating touches issuer records, instrument records, investor-facing disclosures, and historical audit trails simultaneously. Get the workflow wrong, and you’ve got stale data sitting next to a live token that investors are trading against.
How Credit-Rating Changes Enter the Platform Workflow
Credit ratings for Indian corporate bonds come from SEBI-registered credit rating agencies such as CRISIL, ICRA, CARE Ratings, and India Ratings. Under SEBI’s Credit Rating Agencies Regulations, 1999, and subsequent circulars, these agencies publish rating actions through press releases and, for listed debt, through stock exchange disclosure mechanisms. There’s no single universal API that pushes rating changes directly into a platform’s database.
That matters a lot for how you architect ingestion. Some agencies offer licensed data feeds to subscribers. Others publish rating rationale documents on their own websites, with exchanges separately requiring issuers to disclose rating actions under SEBI’s Listing Obligations and Disclosure Requirements (LODR) framework. A platform team has to decide, honestly, which of these sources it can rely on and which require a human in the loop.
Direct agency integration isn’t mandatory, and it isn’t always available either. Many platforms end up with a hybrid model: an automated feed where a commercial agreement exists, plus manual verification against the issuer’s regulatory filing. That hybrid approach isn’t a compromise — it’s often the more defensible design, because it gives you a second source to cross-check against.
Treating a rating feed as “just data” is how platforms end up reconciling bad records six months later. A rating change is an event with provenance, a timestamp, and a scope — design for that, not for a number that overwrites another number.
Distinguishing Direct Feeds From Intermediary Sources
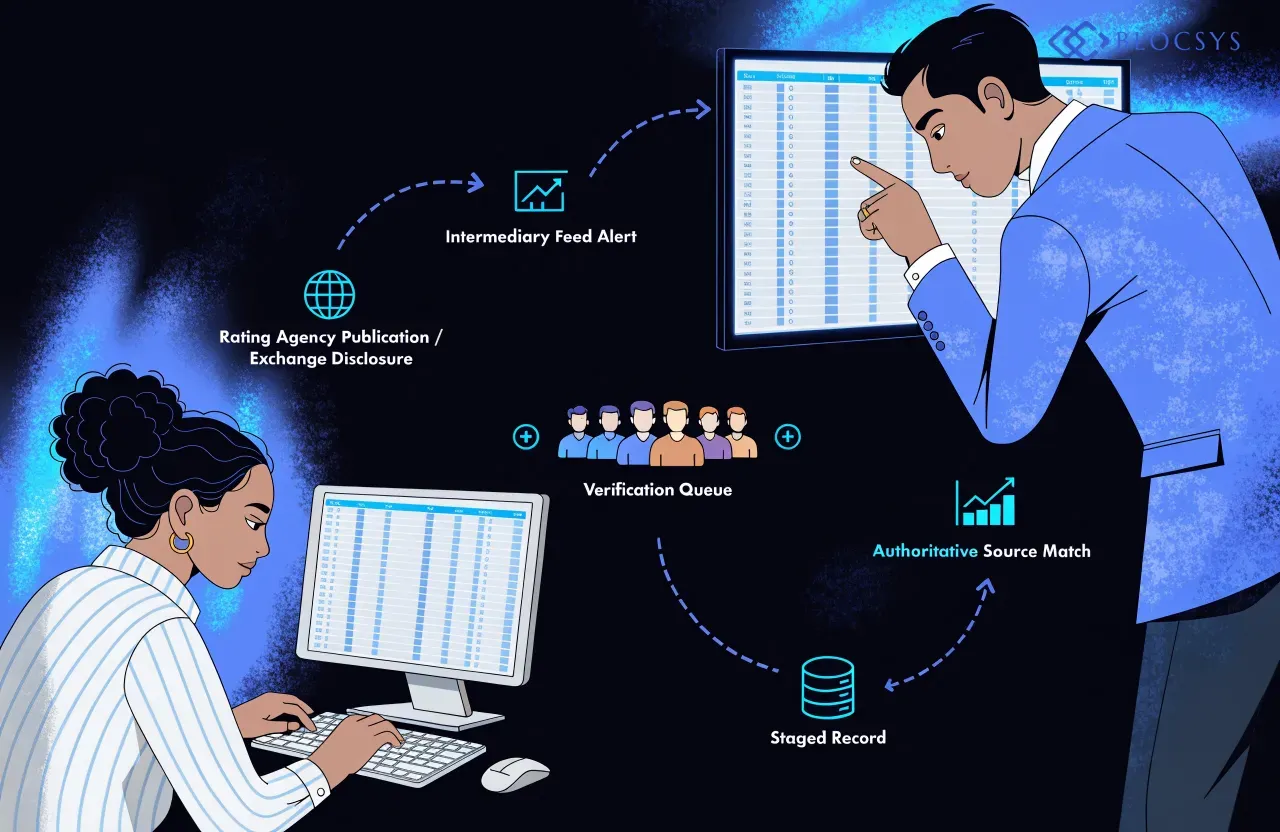
Intermediary sources — financial data vendors, exchange disclosure portals, news wires — often republish rating actions faster than agencies update their own rationale pages. However, speed isn’t the same as authority. A platform that tokenizes corporate bonds should treat the agency’s own published rationale as the authoritative record, and treat faster intermediary signals as early warnings that trigger a verification task, not an automatic update.
Validating Rating Updates Against Issuer and Bond Records
Here’s where most of the real engineering risk sits. A rating action is published against an issuer, or sometimes against a specific instrument or facility. Your platform, meanwhile, tracks individual ISINs. If an issuer has four outstanding bond series and the rating agency revises the issuer’s long-term rating, does that apply to all four tokenized instruments equally?
Not always. Some rating actions apply to specific instruments — secured versus unsecured, senior versus subordinated — while others apply at the issuer level and cascade down. Mapping this correctly requires your platform to maintain a structured relationship between issuer identifiers (such as PAN or CIN) and each ISIN under that issuer, not just a flat issuer-name match.
Name matching alone is unreliable. “ABC Infrastructure Ltd” and “ABC Infrastructure Limited” are the same issuer, but a naive text match might treat them as different. Platforms need deterministic identifier matching — ISIN-to-issuer mapping tables validated against depository records — before any rating update touches a live token record.
Effective Dates Versus Announcement Dates
A rating agency might announce a rating action on one date, with an “outlook” or “watch” designation from an earlier review, and a formal rating letter effective from yet another date. Your platform needs to record all three, because stakeholders asking “when did this rating actually change” deserve a precise answer, not the date your system happened to ingest the feed.
Designing a Reliable Credit-Rating Update Workflow
A workflow that handles rating changes well generally moves through five stages: detection, staging, validation, publication, and notification. Detection means picking up a signal from whichever source you’ve configured. Staging means holding the incoming record separately from the live, trusted record — this single design decision prevents unverified data from touching investor-facing displays.
Validation checks the staged record against issuer-instrument mapping, confirms the source is authoritative or corroborated, and flags conflicts. Only after validation passes does the record move into the published state, where it becomes the system of record for that bond’s current rating. Notification then fires to the relevant audience — issuer teams, compliance, and depending on your disclosure policy, investors.
| Stage | Purpose | Key Decision |
|---|---|---|
| Detection | Capture rating signal from agency, exchange, or vendor feed | Which sources count as triggers versus confirmations |
| Staging | Hold unverified data separately from live records | How long a staged record can sit before escalation |
| Validation | Match issuer/instrument, check authority, flag conflicts | What counts as sufficient corroboration |
| Publication | Update the authoritative rating record and history | On-chain reference versus off-chain full record |
| Notification | Inform relevant stakeholders at appropriate tiers | Who gets real-time alerts versus periodic summaries |
This staged approach is also what makes corporate bond tokenization infrastructure defensible to auditors. You can show exactly when a record moved from unverified to confirmed, and who or what approved that transition.
Managing Delays, Corrections and Conflicting Rating Data
Consider a realistic scenario. A rating agency places an issuer “under watch with negative implications” on a Tuesday. On Thursday, a different data vendor’s feed mislabels this as a formal downgrade. Your platform, if it trusts the vendor feed blindly, publishes an incorrect rating change to a live tokenized bond. Investors see a downgrade that hasn’t actually happened yet.
This is exactly why staging and source hierarchy matter. A “watch” or “outlook” action is categorically different from a confirmed rating change, and your data model needs a field for action type, not just a new rating value overwriting the old one.
Corrections happen too. Agencies occasionally reissue a rating rationale with a corrected effective date or corrected instrument scope. A platform needs an explicit correction path — one that preserves the original (now-superseded) record in history rather than silently deleting it. Otherwise your audit trail has a gap exactly where someone will eventually ask a question.
What Happens When Rating Data Simply Doesn’t Arrive
Delayed updates are common, particularly around holidays or when an agency withdraws a rating due to non-cooperation from the issuer — a distinct SEBI-recognized category. Your platform should distinguish “no update received” from “confirmed unchanged rating,” because treating silence as confirmation is a quiet way to misinform stakeholders.
Rating History, Audit Trails and Stakeholder Notifications
Every rating a bond has carried, not just its current one, belongs in your platform’s historical record. Regulators, auditors, and institutional investors doing diligence will ask for the full trajectory, not a single snapshot. This is where the on-chain versus off-chain decision becomes genuinely important rather than academic.
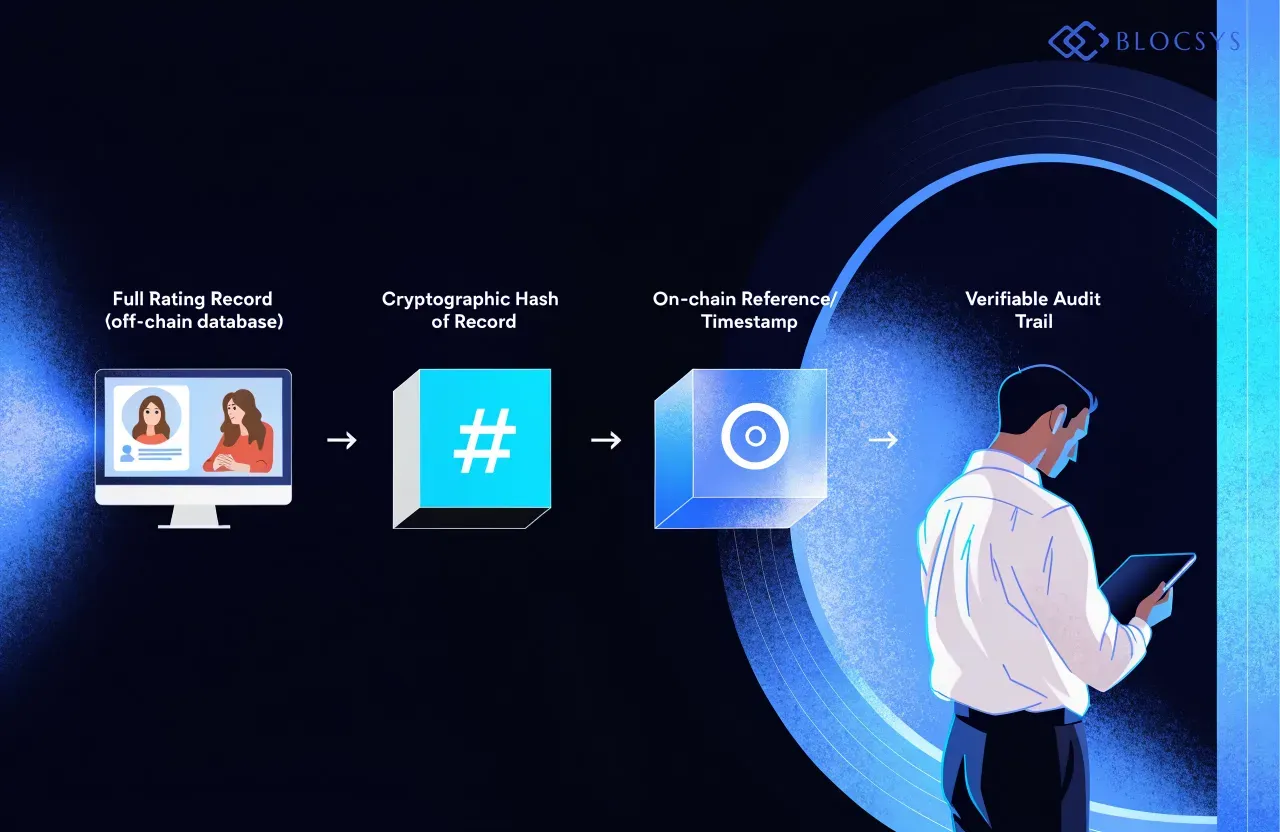
Most teams building tokenized bond infrastructure keep the full rating rationale, supporting documents, and detailed metadata off-chain, while anchoring a hash or reference of each confirmed rating event on-chain. This gives you tamper-evidence without forcing large documents into ledger storage, and it keeps the chain lean while the audit trail stays verifiable.
Notification design shouldn’t assume every stakeholder needs the same alert. A rating downgrade on a widely-held retail bond deserves broader, faster investor communication. A minor outlook revision on an institutional-only placement might only need to reach the issuer relations and compliance teams. Building tiered notification logic — rather than a single broadcast list — keeps the system useful instead of noisy.
A rating downgrade doesn’t automatically trigger a contractual or trading consequence on its own — that depends entirely on the specific bond’s terms, any covenant triggers, and applicable rules. Platforms that hardcode “downgrade equals automatic action” into a smart contract are making a legal assumption their engineering team isn’t qualified to make.
Access Controls Around Rating Records
Not everyone needs write access to rating data. Role-based permissions should separate who can ingest a staged record, who can validate it, and who can approve publication — mirroring the segregation of duties you’d expect in any regulated financial workflow, and documented clearly enough to survive an audit.
Technical Decisions Before Implementing Rating Integration for Corporate Bond Tokenization
Before writing integration code, a platform team should work through several open questions honestly. First: how reliable is each candidate data source, and what’s your fallback when it’s unavailable? Second: does the interface you’re relying on actually support the volume and latency your platform needs, or are you scraping a webpage and calling it an integration?
Third, monitoring. You need alerting for failed ingestion jobs, not just for the ratings themselves — a silent pipeline failure is worse than a slow one, because nobody notices until a stakeholder asks why the displayed rating is three months stale. Fourth, reconciliation: periodically comparing your platform’s stored ratings against a secondary source catches drift before it becomes a dispute.
Finally, decide deliberately what lives on-chain versus off-chain. Full rationale documents, agency commentary, and granular metadata are generally better suited to off-chain storage with proper access controls, while the fact of a rating change, its timestamp, and a verification hash are reasonable candidates for on-chain anchoring. Teams evaluating this trade-off alongside broader platform architecture may find it useful to review how institutional integration requirements shape these same storage decisions, and how reconciliation ties into post-trade reconciliation workflows more broadly.
Building Reliable Credit-Rating Workflows for Bond Tokenization
Handling credit-rating changes well isn’t about chasing the fastest feed. It’s about building a workflow that validates before it publishes, preserves history instead of overwriting it, and notifies the right audience at the right tier. Corporate bond tokenization only earns institutional trust when the data behind each token is as disciplined as the token issuance process itself.
If your team is evaluating how rating-event handling fits into a broader tokenized bond architecture, Blocsys’s work on corporate bond tokenization platform development is a reasonable starting point for mapping these data-integrity requirements against your specific issuer and investor base.
Frequently Asked Questions
Here are direct answers to the questions we hear most often about handling credit-rating changes on tokenized bond platforms.
Does a rating change automatically update a bond’s on-chain record?
Not by default, and it shouldn’t. A reliable workflow stages incoming rating data, validates it against issuer and instrument records, and only then publishes it. Automatic, unvalidated updates risk pushing incorrect or premature data onto a live, investor-facing record.
Is direct integration with a rating agency required for bond tokenization?
No regulation mandates a specific integration method. Platforms commonly combine licensed data feeds where available with manual verification against exchange disclosures or agency rationale documents, since not every agency offers a direct subscription API.
How should conflicting rating announcements be handled?
Treat the rating agency’s own published rationale as the authoritative source, and flag conflicting intermediary signals for manual review rather than auto-publishing either one. Maintaining a source hierarchy prevents a faster but less authoritative feed from overriding confirmed data.
What should happen when a rating update is delayed?
The platform should distinguish “no update received” from “confirmed unchanged,” rather than assuming silence means stability. Flagging overdue checks and surfacing them to compliance teams avoids quietly displaying a stale rating as current.
Should full rating history stay on-chain or off-chain?
Most teams store full rationale and metadata off-chain with controlled access, while anchoring a timestamped reference or hash on-chain for tamper-evidence. This balances auditability with practical storage and performance constraints.
Ready to move beyond theory and build an intelligent platform that delivers real-world value? Blocsys Technologies specialises in engineering enterprise-grade AI and blockchain solutions for the fintech, Web3, and digital asset sectors. Connect with our experts today to discuss your vision and chart a clear path from concept to a secure, scalable reality.